Trusted Platform Module Tpm As Root Of Belief Rot And Cryptographic Options
Weak implementation, poor key lifecycle management, outdated firmware, or misconfigured entry policies can nonetheless create danger. If a microcontroller does not have a Root-Of-Trust built-in, it’s possible to ascertain one using third-party elements, trusted firmware for Cortex-M (TF-M), and so forth. As A Result Of it’s inherently trusted and tamper-resistant, the RoT serves because the secure anchor on which all other safety processes in a tool or system rely. This creates the most devastating type of cybersecurity risk – the Root of Belief (RoT) assaults.
Ideas For Delivering Software Initiatives On-time Every Time
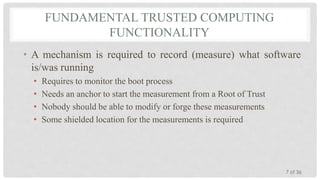
Public and private keys throughout the TPM are utilized for numerous cryptographic operations, attestation, and information safety, contributing to the overall security of the platform. A TPM can present hardware root of trust capabilities, together with secure key storage, platform measurements, and attestation. For secrets and techniques administration, hardware-backed controls cut back the risk of exposing delicate keys, tokens, and credentials.
- The main role of a hardware TPM involves secure storage, key administration, and attestation.
- It serves as the base trusted software program that then authenticates and validates the following piece of software program loaded, which establishes a chain of trust.
- At its core, HRoT establishes a foundational layer of trust within units.
- If any code doesn’t match these signatures, the boot course of halts immediately.
- The following is just a short record of questions that engineers ought to consider earlier than choosing a Root of Trust.
- The security settings will also establish the safety contexts in which the various software elements in the chain of belief are allowed to operate.
Hardware Root Of Belief
For instance, a verified phone number or e-mail address may be used as a trusted fallback if another authentication methodology can not successfully verify the user. Keys are generated contained in the hardware utilizing a certified random number source and by no means go away in plaintext. Cryptographic operations occur inside the module, so the related system receives the completed result while the necessary thing stays inside. Bring Your Individual Key (BYOK) and Maintain Your Individual Key (HYOK) models let organizations and establishments generate and maintain their very own cloud encryption keys as an alternative of delegating that to the provider. Each depend on a hardware root of trust, sometimes an on-premises or customer-controlled HSM, so the root encryption key never resides solely inside the supplier’s infrastructure. The root CA personal secret is probably the most delicate key in any authorities or enterprise PKI.
Cybercriminals are all the time on the lookout for factors with the least resistance or maximum vulnerabilities. The entry factors and the endpoints of the assets are guarded pretty properly, so hackers pivot in the direction of much less seen assault factors just like the Root of Belief. If any of the above is compromised by hackers, everything https://tradeusanews.com/what-are-the-active-security-systems-for-the-car.html, together with VPNs, Multi-Factor Authentication (MFA), browsers, and OS, could be put into chaos.
Uncover Content
Hardware root of trust decisions usually go wrong by mismatching assurance degree to precise danger. Entrust’s HSM purchaser’s guide walks through the way to evaluate FIPS-validated options by surroundings and use case. Support for these algorithms is arriving inside the identical hardware boundary that protects today’s keys, though full FIPS validation for PQC-specific implementations is still rolling out across HSM distributors. Root of Belief assaults are silent killers; they’re refined, making them a harmful threat. They’re designed to strike on the basis of our digital safety stack, undermining the defense layers.

When a system begins up, Secure Boot checks each piece of code towards a database of known good signatures. If any code does not match these signatures, the boot course of halts immediately. As cyber threats evolve, Hardware Root of Trust offers a proactive approach to safeguarding critical techniques. Its implementation creates layers of safety that conventional software options simply can’t match.
Understanding The Position Of Hardware Root Of Trust In Cybersecurity
Moreover, implementing RoT can enhance complexity in gadget design and development. This typically leads to larger costs and longer time-to-market for merchandise that prioritize safety over usability. Learn more about how TypingDNA Confirm 2FA uses typing biometrics and Root of Belief in authentication. Meeting that deadline depends much less on the algorithms themselves, that are already finalized, than on whether or not the hardware defending them may be upgraded to run them.